The steps you may have taken to find 212.32.226.324 include checking a server log, a spam report or a firewall rule. It seems like it’s just like a standard one. It is not. This guide discusses what might cause the 212.32.226.324 address to not validate, how you can verify if this is the case, and what you should do if it is not.
More owners of websites will encounter weird addresses than they would expect. One misleading digit could ruin a rule or distort your figures, and obscure a true visitor. If you understand 212.32.226.324, you can deal with issues quickly and retain your data quality.
What Does 212.32.226.324 Represent?
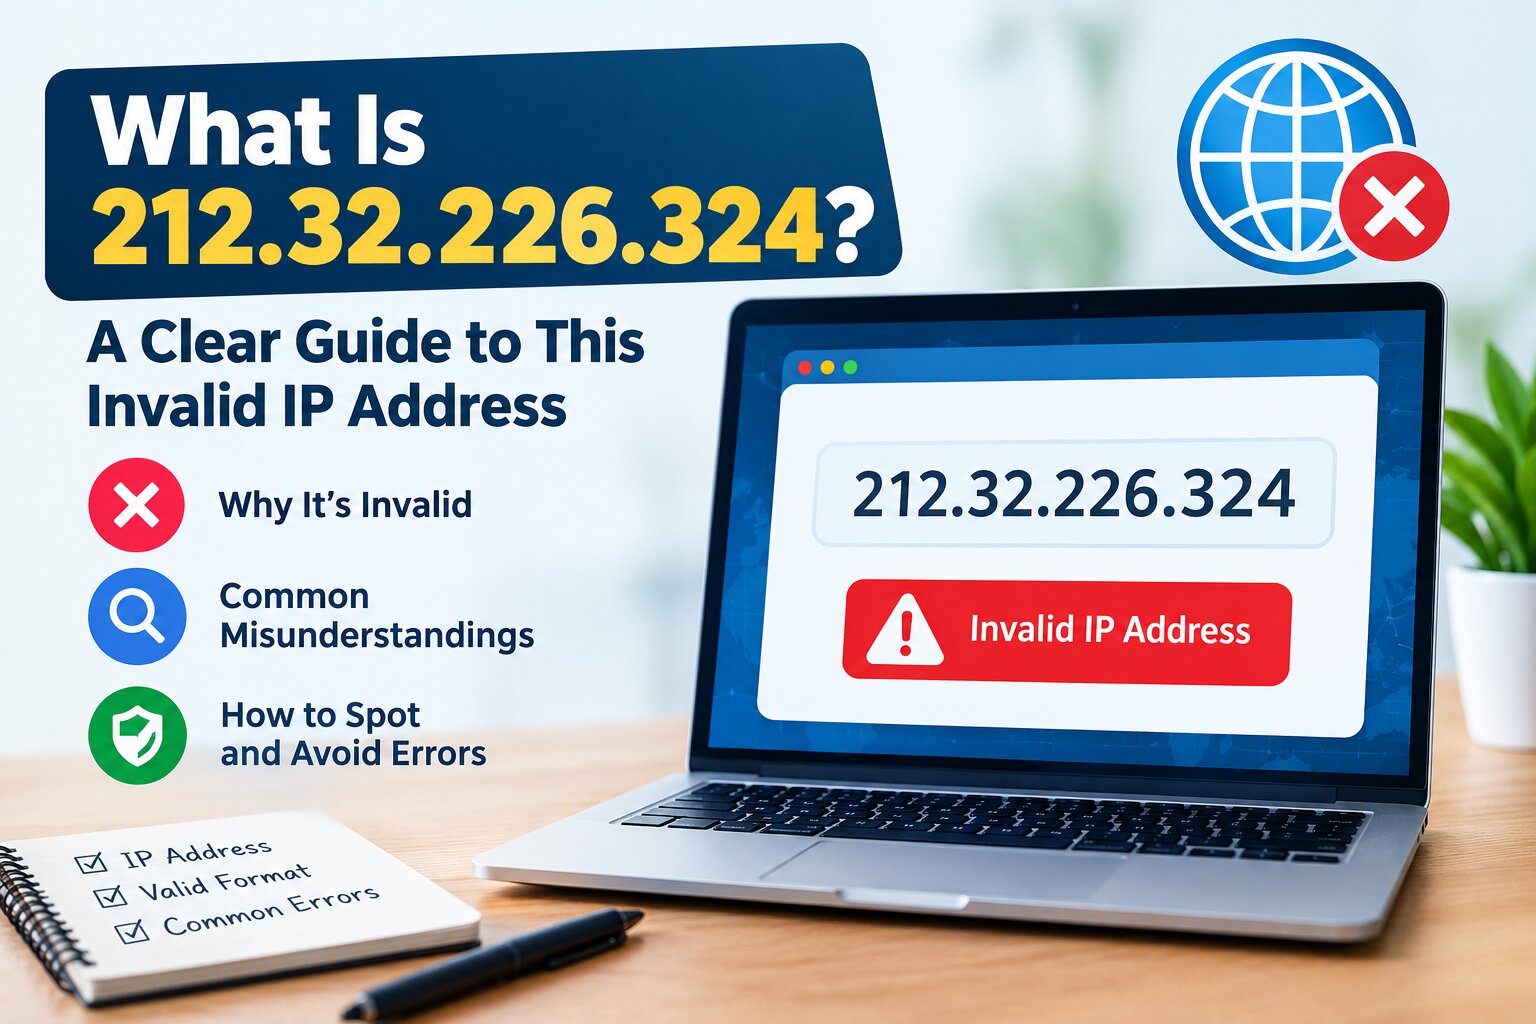
The following string 212.32.226.324 has a dotted representation of an IPv4 address. Has four blocks, dots are used to separate them. It tricks a lot of people and a lot of tools.
An address is not real. There are numeric rules that must be followed for each block. The final block 212.32.226.324 is an exception to those rules and it may never be assigned to be used by any device.
It’s like a phone number – but a digit more. Looks it’s just a glance. This automatic dialer is still not able to dial the phone. This address is treated the same at routers and is not responded to.
It is a common assumption that all dots, which purport to be number strings, refer to actual machines. Assuming that means wasted effort. You can look up an owner, location or a provider. Nothing of those; the address doesn’t exist.
Why 212.32.226.324 Breaks the IPv4 Rules
An IPv4 address with four numbers is octets. 8-bit/8-bit/8-bit/8-bit is used by each octet. The range for each octet is 0-255 due to that limit.
The first three blocks of 212.32.226.324 pass this test. The number 212 is between the numbers. Inside, too, there’s the number 32! It’s also a comfortable number of 226. The number 324 has 69 blocks over the fourth block. An incomplete address automatically makes the whole address invalid.
The value that can be assigned to a host is less than or equal to 255. There’s just no protocol to store it. Routers do not accept a message containing an address of another router just after reading.
Software deals with this failure in various ways. A strict validator will return a direct error. If the text is approved in a relaxed script, then it might not be approved at the end in the strict script. That difference results in bugs that are confusing. Your database may still contain the bad value, as well as your report may continue to report as a real visitor.
How to Test 212.32.226.324 Step by Step
The verification of any suspicious address can take place in less than a minute. First divide the text into segments by the dots. There should be 4 blocks. Red blocks indicate immediately hand on hand problems; green blocks indicate fewer, and yellow blocks indicate more.
Then read out every block as a number. Scan every block to check it is within the range of 0–255. Ignore any block that has letters or symbols sticking out. Strict systems also reject leading zeros (e.g., 012).
Apply this process to 212.32.226.324. There are four blocks and the first 3 pass. There is a fourth block with the value 324, but this doesn’t match the range. The test is complete.
Same logic may be automated for developers. The short regexp is ok, but the built-in network library is better. For instance, ipaddress is a module in the Python library that raises an error for this string at runtime. This is a similar tool provided most modern languages.
Even online lookup services find the same results. They do not return any of those: they do not return any location; they do not return any provider; they do not return any history. An empty result is usually a typographical error and not an indication that they had no user.
Common Sources of 212.32.226.324 in Your Data
It is difficult to get by chance into an invalid address in a pure system. There are general ways that the majority of these errors can be attributed. The fix will depend on the cause so be sure to look for the cause of the issue first.
There are a lot of mistakes involved with manual data entry. Humans incorrectly copy down numbers. Someone changes the “2” to a “3” without anyone knowing about it. This is a mistake commonly made by support teams when they are busy.
Other causes are from bad log parsing. A parsing program can combine numbers within adjacent slots. The obtained output is an address with the extra characters following it. It’s the opposite of established tools – custom scripts fail this way more often.
Another reason is that spam bots also fill fake values. Some bots forge referrer fields and fill them with random numbers. They are looking to add additional pollution to your reports, or luring you into chasing ghosts. These can also appear as real traffic on your analytics reports.
Another source is the test data. Address for demos/staging servers are invented by Developers. The placeholders sometimes end up in the databases themselves. They can be lurking in a forgotten import script and then proliferate across thousands of rows.
What to Do When 212.32.226.324 Appears in Your Logs
Please don’t block this address. If a source is never connected to your server, you cannot use a firewall to filter the traffic from that source. Instead, check out the record.
Use the raw log line as the basis. Do not read just the address column but read the entire entry. Search for some odd sign or fields that are incomplete around the value. Usually the actual reason is shown in the surrounding text.
Finally, make a comparison with other entries in the vicinity. The broken one is an invalid address, but addresses in the vicinity of that address could point to the actual visitor. You might have meant 212.32.226.24 or 212.32.226.224, for example. Those are best regarded as educated assumptions in your case and should be checked for against your records prior to taking action.
Then review your data pipeline. Check each script to modify/insert/remove IP fields. Provide input validation so that poor data values will not be entered to storage. This is the only modification that will ensure that most repeated issues will be avoided.
Lastly, write it down. If the pattern reappears, a little note will make it easier for your team to identify the pattern. Put in the date, source system and any fixes applied.
How 212.32.226.324 Affects Analytics and SEO
Stupid IP address data may appear inconsequential, but it’s taking a toll on your website in subtle ways. Visit Analysis clusters visitors by address. There are visitors who may have more than one entry, which is also inflating unique visitors. They also skew geographical forecasts. Then you base your decisions on biased data.
In addition to this, SEO teams have a challenge to deal with. Crawl logs give you an insight into the actions of search engines. There are also logs of malformed addresses that clutter up those logs. There might be miscommunication about what a bot is doing and several hours might be spent on phantom issues.
Taking charge of the data makes for better rankings. Log files record the pages Googlebot accesses and when, as well as the frequency of access to a specific page. They can also identify sections which will be ignored by search engines. That’s what you use to inform your technical optimization efforts whether it’s the crawl budget or internal linking.
It is important to first delete the garbage like the address 212.32.226.324. Try to do this at all times using filters at the source whenever possible. Otherwise, you should exclude them in the reporting tool. Your conclusions will be based on solid grounds.
Security Risks Linked to 212.32.226.324
It is a false sense of security when creating invalid addresses. Imagine a blocklist that contains 212.32.226.324. The rule was issued for the protection of no one. The list looks complete and is impressive, while real threats go through.
Improper validation is also a key vulnerability targetted by attackers. They pass back values back that are out of shape so you can see what happens. A weak parser could crash, leak an error message or incorrect data into a report or log file. Those are some of the side effects the attacker can use for clues.
Consider all misformed addresses as “signal”. Question the “how” and “why” of how it got to your system. Then make sure the input filters which allow it through are tighter. A robust validation is the thing that makes an innocent error innocuous as well as makes it impenetrable for true intruders.
Examine security rules periodically. Eliminate incorrect data and replace it with correct addresses. Match the rules with a paragraph containing a brief explanation of the rule. Future you will thank you for the clarity.
Travel Networks and 212.32.226.324
Travelers were hardest hit as well by network typos. When guests use guest Wi-Fi at the hotel they will see numbers they don’t recognize on their screens. They type those numbers in to support tickets and ones like 212.32.226.324 move in.
Check all addresses before contacting front desk. Correct details save time and frustration. When managing bookings and working remotely, a reliable internet connection is important.
Planning a stay? Additionally, it is possible to help yourself to save money while you make the repair on your connection. Please verify the latest discount code before making a booking. Browse offers for rooms and packages that are for the season. Smart travellers do some comparison work before they enter into it.
Best Practices to Prevent Errors Like 212.32.226.324
The expenses of prevention are less than cleanup expenses. Take a couple of small tips and implement them into your projects.
Potentially check input at each illustration. Ignore addresses for which an octet is greater than 255. Do this server side only – user can bypass client side checks.
Trust libraries, for validation. Creating your own rules from the ground up provides a ripe environment for errors. There are tools out there that already address cases that you may slip on.
Record both the converted and the raw string. This habit allows you to go back to find where and how errors have been made. It provides you with clarity of the message which the user sent as well as the message which your system accepted it.
Automate your audits. Run the “bad” query regularly against your database to check for invalid data. Share results with your group. Small issues becomes big issues.
Also train colleagues. Prove that they get the right way to read an IPv4 address. Five minutes of lesson now means hours of avoidance of confusion afterward.
Final Thoughts
The string 212.32.226.324 appears to be an IP address, but violates simple IP level rules. It is not safe, since its last number is 324, which is greater than 255. This cannot be used by any device nor can it be routed by any server.
When you find 212.32.226.324 in your data, treat it as a clue. Investigate and fix the raw record, identify the source, and troubleshoot the pipeline. Give the error a check to ensure that the error will not be returned again. Inaccurate address data is a crime – Prevent it.Accurate address data ensures honest reporting and effective security rules.
Recall the lesson to keep in mind. Each octet cannot exceed 255. Always follow that rule if an address seems suspicious.
FAQs
Is 212.32.226.324 a real IP address?
No. The final block (324) is larger than the allowable value of 255. Networks reject 212.32.226.324 as invalid.
Can I trace the location of 212.32.226.324?
No, address does not exist! Loading tools won’t work if it’s not there! Any result for 212.32.226.324 would be unreliable.
Should I block 212.32.226.324 in my firewall?
No. Traffic to this does not pass through your firewall. Look at the log entry (or entries) rather, and correct the root cause of the problem.
Why does 212.32.226.324 appear in my analytics?
Carried over test data, parsing bugs, typos, or spam bots are typically responsible for it. Examine the ‘raw’ log line to pinpoint the cause.
How do I stop invalid entries like 212.32.226.324?
Provide proper validation for every address at entry point. Be sure and use a trusted library; avoid octets greater than 255.